 /Cinny

Posts
22586Following
432Followers
833lotte adds rac- to words a lot but it doesn’t alter meaning
NSFW posts are not for minors (they will be blocked on sight).
Opinions expressed in this profile are representative of those of your employer.
“u are my favorite therianizing biohazard” — @sodiboo@gaysex.cloud
“you know, maybe i will finally learn to read the content warning before clicking 'view' [—] thanks for this lesson @charlotte” — @ariadne@social.treehouse.systems
/Cinny
 repeated

 Ibly 🏳️⚧️


Charlotte /Cinny
charlotte
the world if iocaine was normal instead of wasting resources poisoning opengraph embeds
 0
0
 1
/Cinny
repeated

ira grachevskaya from the hit vn Z.A.T.O. // I Love the World and Everything In It
49016@catgirl.clouddo you have any trust in eMudhra after the 4 incident? glad that at least the RSA certificates were safe?
fear not, here's a complete bypass of their 1fa otp login system. they encrypt OTPs to a public key and issue those behind cloudflare turnstile. this key to be precise:
-----BEGIN PUBLIC KEY-----
MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEA7/OR1az+yTKt1ZONkk+T
owML34smGCo8evpk4zLCsrc+LXtX20yERombX4xh2Sd3VDFML2LuOavB3PwGFfL0
Qr+gGPomq23nqaX9nr5SeSTpFbrxsEEVdipXXpucTFFhnzye7Y7ZodHNQSjUqQPu
L6ktk/YkP0B6k5lIMT//W/4gB3yU1UGCLcSvdMQJo5+I7OdIGxQbir4rtXpdm8qP
3pblFPJXcHc2urBHvJvatUpq/rY0Km4Cxz5ZJwM7MW/hxSRpiTXNoE58W8DHEQVq
ln7RDh0Cc7lA0Qvm92NJIohbi4KZzmq81UA2MyHwyxtkykQxRFO1gEU5i/dp/I5D
ZQIDAQAB
-----END PUBLIC KEY-----
would be a real shame if you can just take that key and """sign""" (encrypt) otp requests yourself :^)
3
12
1
/Cinny
repeated
 /Cinny
repeated

 /Cinny
repeated

Charlotte /Cinny
charlotte
“no way to prevent this”, says only language where this happens regularly
1
1
4
/Cinny
repeated
Krutonium://
krutonium@treehouse.systemsIf you are interested in poking at traffic generated by IoT devices, today would be a good day to ensure that automatic firmware updates are turned off
In other news PHP is FUCKED TURN OFF PUBLIC FACING PHP APPLICATIONS BAD BAD BAD
1
2
1
/Cinny
repeated

Arne Semsrott
arnesemsrott@chaos.socialNEU: Monatelang erklärte die Union, das Informationsfreiheitsgesetz müsse aus Sicherheitsgründen eingeschränkt werden. Sie weigerte sich aber, Belege zu liefern.
Wir verklagten also das Innenministerium, um eine Auskunft zu erzwingen. Ergebnis: Es gibt einfach keine.
https://fragdenstaat.de/artikel/klagen/2026/10/keine-belege/
 0
4
0
/Cinny
repeated

abadidea
0xabad1dea@infosec.exchangeokay, I’m way too late to post xkcd “4” comic and still be funny, so instead I will have to write a serious post
Could this disturbingly severe mistake be because someone asked The Cat for a certificate? Hypothetically, yes. But there’s absolutely no reason to jump to that conclusion with self-righteous confidence when all serious infosec experts have been screaming for THIRTY YEARS that our programming languages are designed to maximize the probability of catastrophic mistakes in cryptographic code even when handled with care by experienced professionals.
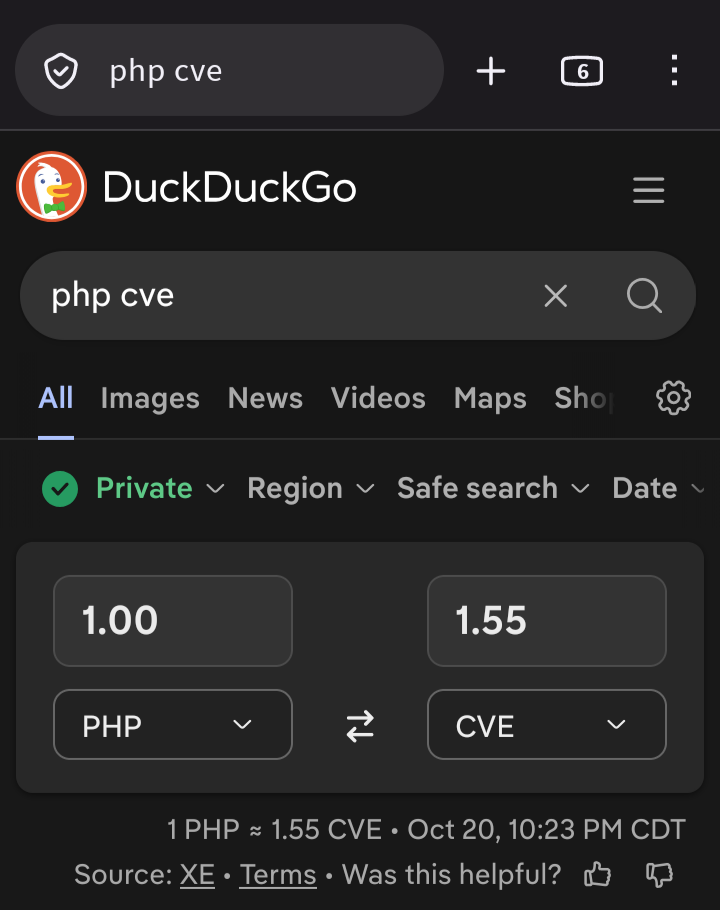
Here’s what we know: several signing certificates from the same issuer with private keys that are, in their entirety, just a number below 256, all the way down to the comical “4, just 4, that’s not a typo, the private key is 4.” This strongly suggests a bug where the first byte of the intended key, treated as an array, was used rather than the whole key. A bug that’s absolutely, positively trivial to write in C and its descendants. I’ve seen proposals for how to gotcha yourself like this in Go as well.
I’m not saying The Cat isn’t involved, it could be. But you absolutely, positively do not have to ask a mischievous clawed agent for a random number for it to go this horribly wrong. We’ve always had the human strength within us to fuck up this bad all along
(And I do assume it’s a fuckup and not a backdoor, because there’s no reason to design a backdoor such that the next random enthusiast to run a sanity check script on public certificates will instantly spot it and start screaming)
10
4
2
Charlotte /Cinny
charlotte
@vxo @philpem baseless conspiracy theories are not welcome here, this is a mistake one reasonably could have made (ideally not in this fucking situation though) while a government in a position to enforce such a limitation on elliptic curve key generation to a security level of 8 bits (!) would have also been able to demand the private key or demand the company to sign stuff with said private key. this way anyone could have found and exploited the backdoor easily, which is not what authoritarian governments would want
1
0
1
Charlotte /Cinny
charlotte
how do you even recover from “our really shitty hand-rolled ecdsa accidentally only includes 1 byte of randomness as the least significant byte” as a company that sells encryption to governments
3
12
37